
promptsite
v0.4.0
Published
One sentence to an audited, ready-to-deploy website: generate a multi-page site with your own model, edit it visually, block leaked secrets, and deploy to Cloudflare Pages or Netlify.

Maintainers
 vaibhavbansal26
Readme
promptsite
From one sentence to a deployable website, with your own model and your own files.
export ANTHROPIC_API_KEY=sk-ant-...      # your key, read from the environment, never stored

npx promptsite generate "Family bakery in Leeds, sourdough and custom cakes, order online" --template local-business --out ./bakery
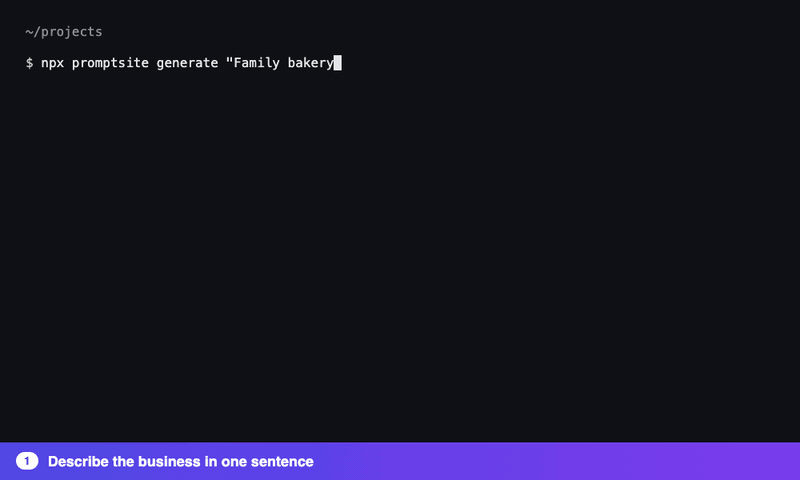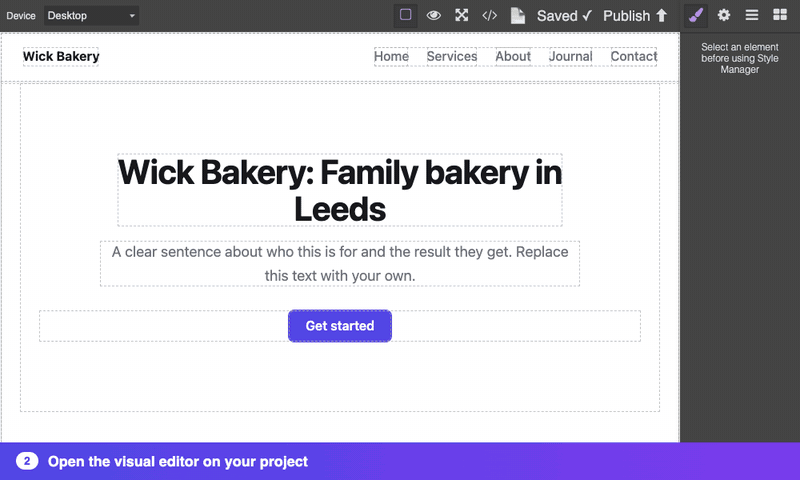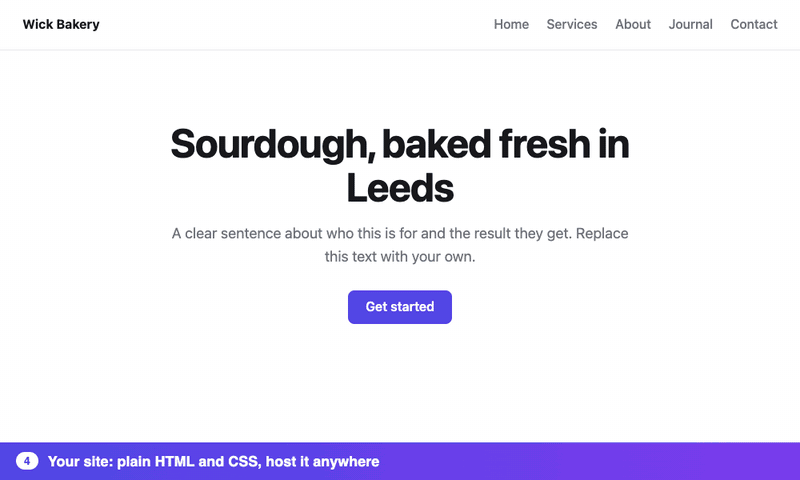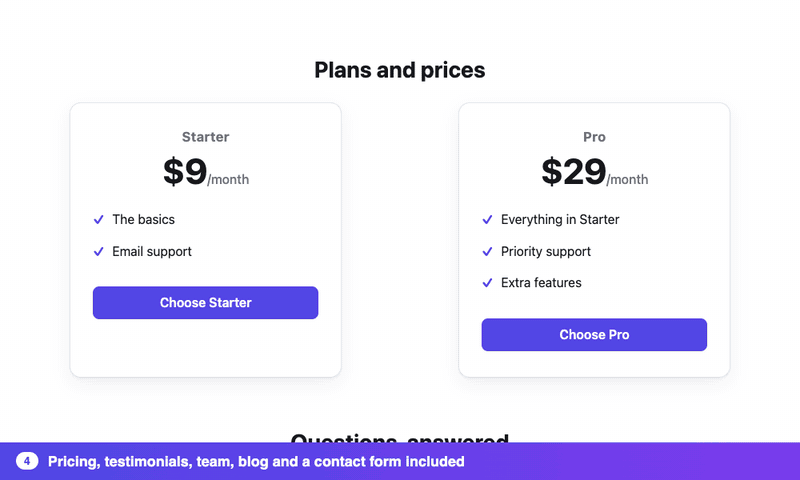
npx promptsite edit ./bakery             # polish it visually at http://127.0.0.1:4173, then press Publish
You get an editable project plus plain static HTML, CSS and JS (no framework, no inline code, works under a strict CSP): multi-page, with a working contact form, optional Stripe checkout buttons, and a brand colour of your choice. No key yet? Add --provider mock to try the whole pipeline offline.
The model writes validated JSON copy, not markup. Templates render that copy into the blocks of grapesjs-advance-components and escape every string, so the output is safe by construction and fully editable afterwards.
📖 Documentation · 🧪 Try the editor in your browser
Commands
| Command | Does |
|---|---|
| promptsite generate "<brief>" | Draft a multi-page site and write it to a folder |
| promptsite edit <dir> | Visual editor on localhost (autosave, Publish writes public/) |
| promptsite build <dir> | Re-render project.json to public/ (for CI) |
| promptsite audit <dir> | Scan a site or any folder for leaked secrets and unsafe markup |
| promptsite deploy <dir> --to cloudflare\|netlify | Audit, then publish to Cloudflare Pages or Netlify (a leak stops it) |
| promptsite serve --root <dir> | HTTP API for n8n, Zapier or cron (needs PROMPTSITE_API_TOKEN) |
| promptsite templates | List the templates |
Templates: landing (Home, Pricing, Contact), local-business (Home, About, Contact), small-business (Home, Services, About, Journal, Contact: testimonials, pricing, FAQ, team and a blog list), shop (Home with Stripe buttons, Contact).
Useful flags: --name, --accent "#0d9488", --theme dark, --payment-link <Stripe Payment Link>, --form-endpoint <url>, --provider anthropic|endpoint|mock, --endpoint <your backend>, --model <id>. Run promptsite --help for all of them.
bakery/
  project.json        the editable GrapesJS project
  promptsite.json     your settings (never a secret)
  public/             index.html, about.html, contact.html + .css + .js + _headers (strict CSP)
Security
Nothing reaches disk or a browser that looks like a secret:
- Keys stay in the environment.
ANTHROPIC_API_KEYandPROMPTSITE_API_TOKENare never read from flags or written to files. The editor's ✨ button calls the model through the local server. - Fail-closed scan. Anthropic, OpenAI, Stripe secret, GitHub, AWS and Slack keys, private keys, credentials or secret-looking parameters in URLs,
javascript:URLs, inline handlers and plain-http forms stopgenerate,build, the editor's Save/Publish and the API. Findings are shown redacted.--allow <rule>is the explicit opt-out. - Redacted logs. Errors are stripped of key formats and of the exact key values in use.
- Strict CSP. Exports include a
_headersfile (Netlify, Cloudflare Pages): no inline script or style,connect-srclimited to your form endpoint. - Closed servers.
editandservelisten on loopback only.serveneeds a 24+ character bearer token, throttles failures, rejects browser requests, caps body size, jobs and hourly volume, and confines each site to its own folder.editrejects any foreignHostorOrigin.
npx promptsite audit ./bakery --strict # fail CI on a leak or unsafe markupWhat cannot be promised: everything in a static site is public (form endpoints, Payment Links); a webhook URL, including an n8n one, is a bearer credential; the scanner is heuristic; and your brief goes to the model provider. Details in SECURITY.md.
Automation (n8n, CI)
export PROMPTSITE_API_TOKEN="$(openssl rand -hex 24)"
npx promptsite serve --root ./sites      # http://127.0.0.1:8787
POST /v1/generate, /v1/build, /v1/audit, GET /v1/sites and /v1/sites/<slug>/bundle.zip, all with Authorization: Bearer $PROMPTSITE_API_TOKEN. An importable n8n workflow (webhook → generate → audit → respond) is in examples/n8n; it is written from n8n's documented formats and structure-tested, but has not been run inside n8n.
# CI
- run: npx promptsite build ./site && npx promptsite audit ./site --strict
Deploy
export CLOUDFLARE_API_TOKEN=... CLOUDFLARE_ACCOUNT_ID=...
npx promptsite deploy ./bakery --to cloudflare --project my-site --branch main

export NETLIFY_AUTH_TOKEN=...
npx promptsite deploy ./bakery --to netlify --project <site-id> --prod

npx promptsite deploy ./bakery --to cloudflare --project my-site --dry-run   # show the command, deploy nothing
It runs the audit first and stops on a leaked key, then runs wrangler@4 or netlify-cli@27 with the token taken from the environment (tokens are never flags). Both need Node 22+. Netlify makes a draft URL unless you add --prod; on Cloudflare the project's production branch goes live. To try it safely: start with --dry-run, then a throwaway project and a token scoped to it, then revoke the token. The step-by-step, common errors and CI and n8n recipes are in the docs.
Honest limits
- The copy is a draft. Prices and testimonials are placeholders the tool tells you to replace, and it never invents facts you did not give it.
- Tested end to end with the mock provider and a fake API server; output quality with a live model depends on the model and your brief.
- Pages have no images yet.
public/is plain files for any static host, andpromptsite deploypublishes them to Cloudflare Pages or Netlify (tested with a fake runner, not yet run against a real account by the author). - Needs Node 18 or newer. The first run installs
jsdomandgrapesjs(the plugin renders in a headless editor).
Development
npm install                        # at the repo root
npm test -w promptsite
npm run build                      # plugin first, then the CLI
License
MIT