
shadowbox-cli
v0.1.2
Published
Zero-trust copy-on-write sandbox and interactive time-machine for AI coding agents

Maintainers
 nari_ab
Readme
ShadowBox runs autonomous AI coding agents (Claude Code, Cursor, Aider, OpenHands) inside an ephemeral copy-on-write scratchpad on macOS and Linux. It strips secret credentials before the agent process spawns, isolates file mutations on an APFS zero-copy layer, and lets you review or discard changes before anything touches your real repository.
Quick Start
Run immediately with zero prior installation:
npx shadowbox-cli claudeOr install globally:
npm install -g shadowbox-cli
shadowbox aider
Requires macOS (APFS) or Linux.
Interactive Session
shadowbox session — zero-trust copy-on-write runtime

2 file(s) modified in sandbox:
  ● [A] src/auth/jwt.ts (+38 lines)
  ● [M] package.json (+1 line)

SECRETS BLOCKED (3)
  ● AWS_SECRET_ACCESS_KEY — stripped from process env
  ● GITHUB_TOKEN          — stripped from process env
  ● .env                  — masked with [SHADOWBOX_REDACTED]

HOST REPOSITORY
  ● 100% untouched, 0 unapproved writes

CONTROLS
  [c] Commit approved changes to host
  [q] Discard sandbox and leave host untouched
  [Tab] Toggle diff viewer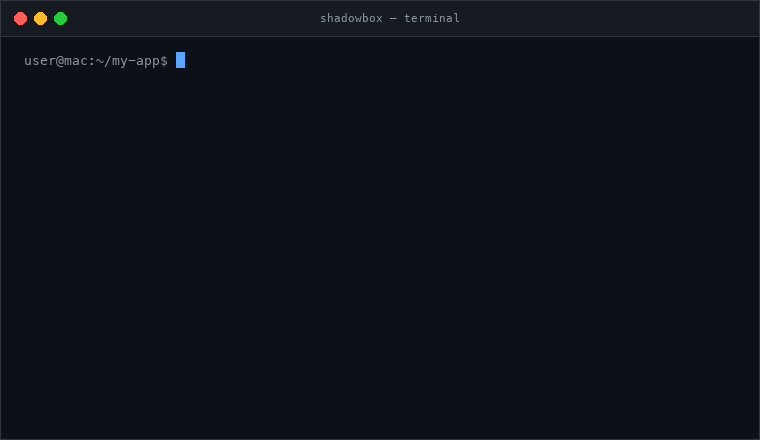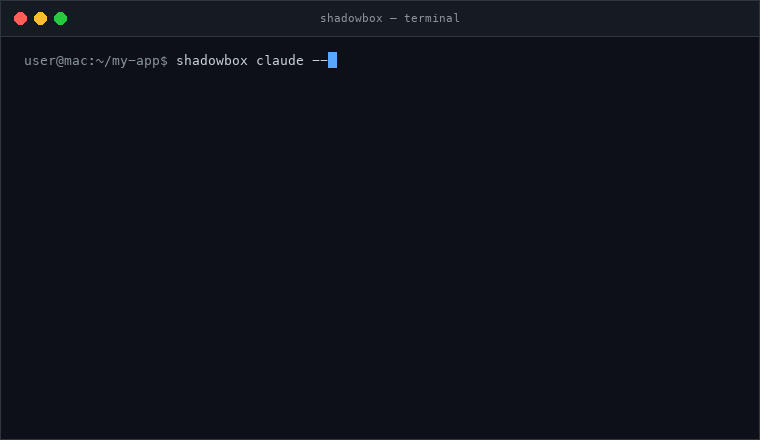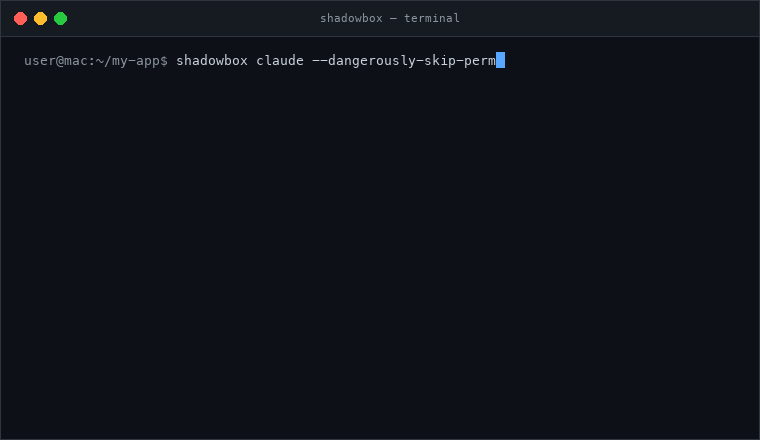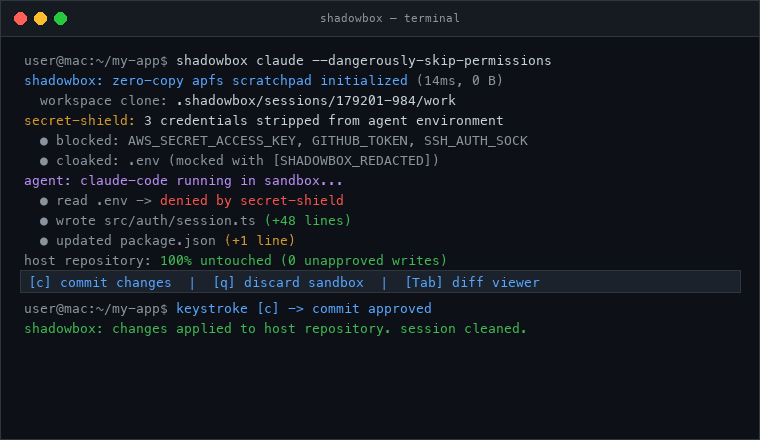
Key Features
- Zero-Copy CoW. Uses APFS
clonefile()on macOS. Clones a 50,000-file project in ~14ms with 0 bytes additional disk usage. Real files remain untouched until you commit. - SecretShield. Strips sensitive env vars (
AWS_*,SSH_*,GITHUB_TOKEN,DATABASE_URL) from the agent's process environment and cloaks.envfiles with harmless mocks. - One-key rollback. Interactive dual-pane TUI or headless mode. Commit with
[c], abort and wipe with[q].